You Have 100 Passwords and You Remember Zero of Them
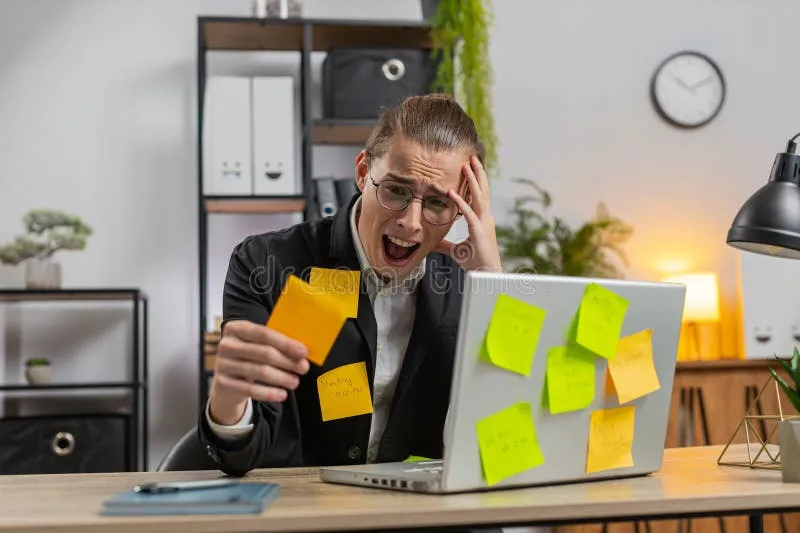
Photo: person frustrated at laptop with sticky notes on computer screen passwords, via thumbs.dreamstime.com
Somewhere between creating a Petco rewards account and signing up for that one recipe newsletter you read exactly once, something broke. Not your WiFi. Not your laptop. Your brain.
According to research from NordPass, the average internet user now manages somewhere north of 100 online accounts. One hundred. That's more passwords than most people have had first dates, job interviews, or dentist appointments combined. And yet every single one of those accounts is technically asking you to remember a unique, complex, never-repeated string of characters — ideally something like Tr0ub4dor&3, not your dog's name followed by your birth year.
Spoiler: it's mostly the dog's name.
The Moment We All Got Buried
It didn't happen overnight, but it kind of feels like it did. Think back to 2005. You probably had an email address, maybe a MySpace, and a bank login. That was it. Password management was a non-issue because there was barely anything to manage.
Fast forward to today and the average American has accounts scattered across streaming platforms, food delivery apps, airline loyalty programs, work tools, social media, shopping sites, healthcare portals, government services, and approximately forty-seven apps they downloaded once and never opened again. Each one came with a registration screen, a verification email, and the cheerful demand to "create a secure password."
Cognitive psychologists have a term for what happens when we're forced to track too many pieces of information: cognitive overload. Dr. Lisa Feldman Barrett, a neuroscientist at Northeastern University, has written extensively about how the brain prioritizes emotional relevance and repetition when forming memories. A password for a site you visit twice a year? Your brain has zero incentive to hold onto that. It's digital white noise.
So we forget. And then we click "Forgot Password." Over and over again.
The Statistics Are Genuinely Embarrassing
Here's where it gets both funny and alarming. A 2023 study by Beyond Identity found that 55% of Americans have abandoned an online purchase simply because they couldn't remember their login credentials. Not because they changed their mind. Not because they found a better deal. Because they couldn't get past the front door.
Another survey by Google revealed that one in three Americans reuses the same password across multiple accounts. Security experts will tell you this is roughly equivalent to using the same key for your house, your car, your office, and your gym locker — and then taping a copy of that key to your front window.
And yet, here we are.
How People Are Actually Coping (Brace Yourself)
So what does the average person actually do when faced with 100+ login credentials? The answers range from reasonably smart to "please don't ever do this."
The Post-it Note Method Yes, it's real. A surprisingly large number of Americans — particularly older generations — write passwords on physical paper. Sometimes it's a notebook. Sometimes it's a sticky note on the monitor. Sometimes it's a piece of paper tucked inside a physical wallet. Security researchers universally hate this. But honestly? If someone has to physically break into your home to steal your Netflix password, the threat model is pretty specific.
The Spreadsheet System Slightly more sophisticated, and wildly more common than you'd think. People build elaborate Excel or Google Sheets documents to catalog their accounts. Some even color-code them. The problem, of course, is that a Google Sheet is itself behind a password. And if that account gets compromised, so does everything else. It's turtles all the way down.
The Recycler This is the most common approach and the most dangerous. People pick one or two "base" passwords and rotate minor variations — capitalizing a letter here, adding an exclamation point there. Hackers know this. There's an entire category of attack called credential stuffing that specifically exploits recycled passwords. If your email password leaks in a breach (and statistically, it already has — check HaveIBeenPwned.com), attackers will try that same password on your bank, your Amazon account, and everything else.
The Password Manager Convert This is the crowd that discovered tools like 1Password, Bitwarden, or Apple's built-in Keychain and genuinely had a religious experience. Password managers generate unique, random, impossibly complex passwords for every site and store them behind a single master password. Security experts love this approach. Adoption is growing but still relatively low — around 30% of Americans use one, according to Security.org.
The "Just Use Google" Crowd A growing segment of the population has essentially outsourced their entire digital identity to Google or Apple, relying on single sign-on options wherever possible. It's convenient. It's also a massive single point of failure. If that Google account ever gets locked or compromised, the digital house of cards collapses entirely.
The Psychology of "I'll Fix It Later"
Here's the thing nobody wants to admit: most people know their password habits are bad. They've read the articles. They've seen the breach notifications. They've watched the "change your password" warnings pile up in their inbox like unread newsletters.
And they still don't fix it.
Psychologists call this the intention-behavior gap — the space between knowing what you should do and actually doing it. When it comes to passwords, the gap is a chasm. Changing 100 passwords is an enormous, tedious task with no immediate reward. The risk feels abstract until it doesn't — until the morning you wake up to a fraudulent charge or a locked account.
There's also something called security fatigue, a term the National Institute of Standards and Technology (NIST) has actually used in official documentation. When people are bombarded with too many security demands — update this, verify that, enable two-factor here — they start tuning it all out. The brain treats it like background noise. The warnings stop registering.
Is There Actually a Fix?
The honest answer is: kind of, and it requires a little effort up front.
Security professionals consistently recommend the same short list of actions: use a password manager, enable two-factor authentication on your most important accounts (email, banking, social media), and stop reusing passwords. That's genuinely most of it.
Passkeys — a newer technology being pushed by Apple, Google, and Microsoft — may eventually replace passwords entirely, using biometric authentication instead. But widespread adoption is still years away for most everyday users.
In the meantime, the digital graveyard keeps growing. Somewhere out there, a forgotten Myspace account still exists with a password you set in 2007. A Blockbuster Online account with your old address. A fitness app from a New Year's resolution you abandoned by February.
All of it, just waiting for someone — hopefully you, not a hacker — to eventually clean it up.
No pressure, though. You can always do it later.